
Microsoft Account Compromised in Crypto Pump-and-Dump Scheme
On Thursday, the official Microsoft account on X, which boasts over 13 million followers, fell victim to a security breach. Attackers took control of the account to promote a cryptocurrency scam involving a token called $Clippy, marking a significant incident tied to cybercrime in the cryptocurrency realm.
Incident Overview
The breach initiated when the compromised account (@Microsoft) began following and retweeting from a now-suspended account called @clippymsftcto, which falsely portrayed Microsoft’s Clippy virtual assistant. Although the impersonating account has since been suspended, another account named @ClippyMSFT continues to advertise the fraudulent $Clippy crypto token, misleading users with claims about an association with Microsoft stock.
Microsoft has responded swiftly by removing unauthorized posts from their account and launched an investigation into the breach. A Microsoft spokesperson stated, “We have confirmed unauthorized access to our account on X including posts that did not come from Microsoft.” They assured users that appropriate security measures have been implemented and that the investigation is ongoing.
Microsoft’s Response
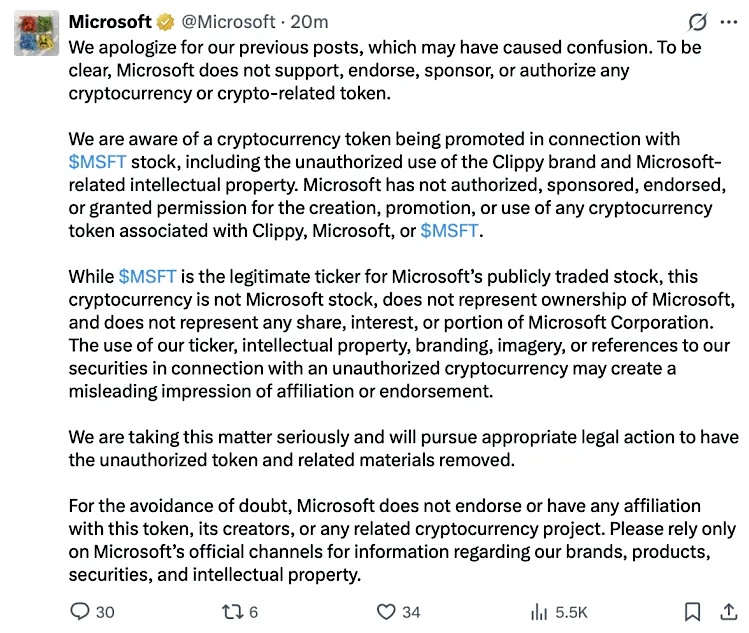
In an official statement, Microsoft expressed its disapproval of the scam, clarifying, “We are aware of a cryptocurrency token being promoted in connection with $MSFT stock, including the unauthorized use of the Clippy brand and Microsoft-related intellectual property.” They further emphasized their lack of endorsement for the cryptocurrency and their intention to pursue legal action against the perpetrators.
History of Account Hijacking
This event is not Microsoft’s first experience with account hijacking on X. In June 2024, the Microsoft India account (@MicrosoftIndia) was similarly compromised. Scammers impersonated meme stock trader Keith Gill to lure followers into malicious schemes, resulting in substantial theft through a cryptocurrency wallet drain.
The frequency of such scams on X has raised alarms. Recent analysis by blockchain security experts at ScamSniffer indicated that approximately $59 million in cryptocurrency was stolen from 63,000 individuals during a single promotional campaign involving hackers using the “MS Drainer” wallet drainer.
Broader Implications
Account hijacking remains a significant threat to verified organizations on social media platforms, often resulting in substantial financial loss for unsuspecting users. For instance, the U.S. Securities and Exchange Commission’s (@SECGov) account was taken over in a SIM-swapping attack, where hackers shared a fictitious announcement regarding Bitcoin exchange-traded funds, subsequently causing a spike in Bitcoin prices. Eric Council Jr., responsible for this incident, pleaded guilty to charges related to his role in manipulating Bitcoin’s value and received a 14-month prison sentence in early 2025.
Conclusion
The incident involving Microsoft illustrates the ongoing danger posed by cybercriminals in the social media landscape. With accounts being hijacked to promote scams, organizations and users alike must remain vigilant to avoid falling prey to such exploits.
